


Hi everyone!
Some days ago, I confronted to a hard problem and I could not solve it. Can you help me?
The problem was: Given a and n(1 <= a, n <= 1000). And b = (a ^ a) ^ (a ^ a). And return b mod n.
| # | User | Rating |
|---|---|---|
| 1 | Benq | 3676 |
| 2 | Kevin114514 | 3659 |
| 3 | jiangly | 3640 |
| 4 | turmax | 3450 |
| 5 | tourist | 3382 |
| 6 | strapple | 3360 |
| 7 | Um_nik | 3354 |
| 8 | squareOf105 | 3348 |
| 9 | maroonrk | 3312 |
| 10 | idontwannadothis…e | 3191 |
| # | User | Contrib. |
|---|---|---|
| 1 | Qingyu | 155 |
| 2 | nik_exists | 151 |
| 3 | maspy | 149 |
| 4 | AmShZ | 145 |
| 5 | Um_nik | 143 |
| 6 | Errichto | 139 |
| 7 | BledDest | 136 |
| 8 | adamant | 134 |
| 9 | maroonrk | 132 |
| 10 | cry | 130 |
Hi everyone!
Some days ago, I confronted to a hard problem and I could not solve it. Can you help me?
The problem was: Given a and n(1 <= a, n <= 1000). And b = (a ^ a) ^ (a ^ a). And return b mod n.


Auto comment: topic has been updated by VIIIIIIVX (previous revision, new revision, compare).
Use a^phi(n) is 1 mod n. Find a^a mod n, and a^a mod phi(n).
This is valid only if a and n are co — prime,and he has not mentioned so in the blog
True that. If that's not true, then that's some real trouble. Maybe this helps in that case.
Incase a, n are co-prime, I guess this will work.
You can use Euler's Theorem for xy % n even when gcd(x, n) ≠ 1. This requires that the residue used in the exponentiation is equal or bigger than the highest power of the prime powers shared by x and n. So in such case, find y % φ(n) until the value is the smallest value greater or equal to the highest power of the prime factors shared by x and n.
Having said this, in above case the highest shared power is ≤ 10. So calculations then can fit in long long.
A simple way is to compute the values 1, a, a2, a3, ... modulo n until you find a loop. Due to non-coprimeness issues, it may not end in 1, so it has the so-called ρ structure (a tail and a cycle). Still, we know the start of the cycle and its period, so we can reduce the exponent modulo this period.
So now we have to compute the exponent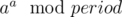 . This can be done straightforwardly or using fast exponentiation.
Oh yes yes, thans a lot!