


Lets say I have a Big Integer A and an integer B . I want to calculate A mod B in O(number_of_digits_in(A)) complexity.
How can I do that?
| # | User | Rating |
|---|---|---|
| 1 | Benq | 3676 |
| 2 | Kevin114514 | 3659 |
| 3 | jiangly | 3640 |
| 4 | turmax | 3450 |
| 5 | tourist | 3382 |
| 6 | strapple | 3360 |
| 7 | Um_nik | 3354 |
| 8 | squareOf105 | 3348 |
| 9 | maroonrk | 3312 |
| 10 | idontwannadothis…e | 3191 |
| # | User | Contrib. |
|---|---|---|
| 1 | Qingyu | 155 |
| 2 | nik_exists | 151 |
| 3 | maspy | 149 |
| 4 | AmShZ | 145 |
| 5 | Um_nik | 143 |
| 6 | Errichto | 139 |
| 7 | BledDest | 136 |
| 8 | adamant | 134 |
| 9 | maroonrk | 132 |
| 10 | cry | 130 |
Lets say I have a Big Integer A and an integer B . I want to calculate A mod B in O(number_of_digits_in(A)) complexity.
How can I do that?


Modular arithmetic is a great help here.
Let's say that A = 10k - 1·ak - 1 + 10k - 2·ak - 2 + ... + 100·a0, where ai are digits of A. You have to calculate that expression modulo B. Note that you can easily calculate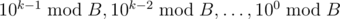 in linear time: just start with 100 = 1 and then multiply by ten (and apply modulo afterwards) until you have all k values. Now the expression is slightly simpler: you only have small numbers, so you can just calculate it straightforwardly, applying modulo after each operation.
Another approach: A = a0 + 10·(a2 + 10·(... + 10·(ak - 1)...)). You start calculating that expression from inside: ak - 1, then you multiply it by ten and add ak - 2, and so on until a0.