


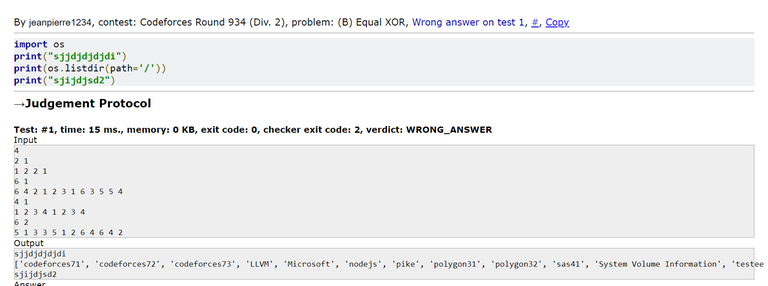
I decided to browse Codeforce submission for a question that I completed and I saw this. I doubt this guy will do much harm but I still find it quite funny.
→ Обратите внимание
→ Лидеры (рейтинг)
| № | Пользователь | Рейтинг |
|---|---|---|
| 1 | Benq | 3676 |
| 2 | Kevin114514 | 3659 |
| 3 | jiangly | 3640 |
| 4 | turmax | 3450 |
| 5 | tourist | 3408 |
| 6 | strapple | 3360 |
| 7 | Um_nik | 3354 |
| 8 | squareOf105 | 3348 |
| 9 | maroonrk | 3312 |
| 10 | idontwannadothis…e | 3191 |
| Страны | Города | Организации | Всё → |
→ Лидеры (вклад)
| № | Пользователь | Вклад |
|---|---|---|
| 1 | Qingyu | 154 |
| 2 | nik_exists | 151 |
| 3 | maspy | 149 |
| 4 | AmShZ | 146 |
| 5 | Um_nik | 143 |
| 6 | Errichto | 139 |
| 7 | BledDest | 136 |
| 8 | adamant | 135 |
| 9 | maroonrk | 133 |
| 10 | cry | 130 |
→ Найти пользователя
→ Прямой эфир


Codeforces (c) Copyright 2010-2026 Михаил Мирзаянов
Соревнования по программированию 2.0
Время на сервере: 09.11.2026 23:08:39 (g2).
Десктопная версия, переключиться на мобильную.
При поддержке


Auto comment: topic has been updated by HatedFate (previous revision, new revision, compare).
Auto comment: topic has been updated by HatedFate (previous revision, new revision, compare).
Lol. seems like someone is trying to practice "Command Injection" on codeforces xD
Possibly tell him that hacking sites without permission is illegal before he gets in trouble.
Edit: nvm this was all 3 months ago. It looks like he ended up sending messages from cf servers using python's socket library. I wonder why the admins haven't disabled such libraries.
The way to address this is not to disable the libraries, the way to address this is to block network access (relevant syscalls or similar), preferably by using a proper sandbox.
I didn't believe this would actually make a request but it does. I tried this: 265945617 and sure enough, it actually made a request, there is a log event of that on my server.
EDIT: and it can receive too! 265946029 I think this might actually turn out to be a serious vulnerability.
So theoretically you could send over test data to a private server that could run embarrassingly parallel code on a cluster (let's say, running $$$O(n!)$$$ when the intended is $$$O(\textsf{poly}(n) 2^n)$$$) and print the result to CF stdout?
Seems like an even more cursed way of solving Watermelon!
theoretically speaking, you can basically write a script to do so, for a non-interactive problem at least, so basically someone can get the full systests, if he just tries so many directories to finally find the systest folder...