


How can I find modular multiplicative inverses of a range in linear time?
→ Обратите внимание
→ Трансляции
→ Лидеры (рейтинг)
| № | Пользователь | Рейтинг |
|---|---|---|
| 1 | jiangly | 3810 |
| 2 | Benq | 3676 |
| 3 | Kevin114514 | 3655 |
| 4 | maroonrk | 3463 |
| 5 | strapple | 3447 |
| 6 | Um_nik | 3387 |
| 7 | heuristica | 3322 |
| 8 | turmax | 3317 |
| 9 | tourist | 3307 |
| 10 | jiangbowen | 3291 |
| Страны | Города | Организации | Всё → |
→ Лидеры (вклад)
| № | Пользователь | Вклад |
|---|---|---|
| 1 | Qingyu | 156 |
| 2 | nik_exists | 150 |
| 2 | maspy | 150 |
| 4 | Um_nik | 141 |
| 5 | Errichto | 139 |
| 6 | adamant | 137 |
| 7 | AmShZ | 135 |
| 8 | BledDest | 132 |
| 9 | maroonrk | 131 |
| 10 | qwexd | 129 |
→ Найти пользователя
→ Прямой эфир


Codeforces (c) Copyright 2010-2026 Михаил Мирзаянов
Соревнования по программированию 2.0
Время на сервере: 25.09.2026 01:19:48 (g2).
Десктопная версия, переключиться на мобильную.
При поддержке


Do you want to find a multiplicative inverse for all numbers from 1 to N — 1?
It can be easily done for a prime N, the idea should be obvious if you'll read about primitive roots modulo N.
For non-prime N the idea should also be similar.
I read about primitive roots that -
If the prime number is p, a primitive root g is a number, that when n goes from [1...p - 1], then gn mod p goes through all the numbers [1...p - 1] in some order.
How do I utilize this further? Sorry but I am unable to really understand how to form a relation between modular inverse and primitive root.
If you thought harder, you'd come up with an idea :).
Due to Fermat's Little Theorem: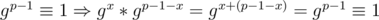 .
if the number with respect to which you are finding the modular inverse (i.e. the 'M' in A%M is prime)you can use the Fermat's little theorem according to which the modular inverse of a number with respect to a prime number (say A and P respectively) is pow(A,P-2)
so in one for loop you may find the modular multiplicative inverses of the numbers in the range but the complexity is O(nlogp) as the power function takes log(p) time
http://e-maxx.ru/algo/reverse_element#4 (it's in russian but you can see the code)
Can you please explain the last step before QED in the proof provided?
What have they done after taking mod m on both sides?
They've multiplied both sides of the equality by
r[i] * r[m mod i].